CVE-2026-90843
CVSS:4.0/AV:N/AC:L/AT:N/PR:N/UI:N/VC:L/VI:L/VA:L/SC:L/SI:L/SA:L/E:P
Summary
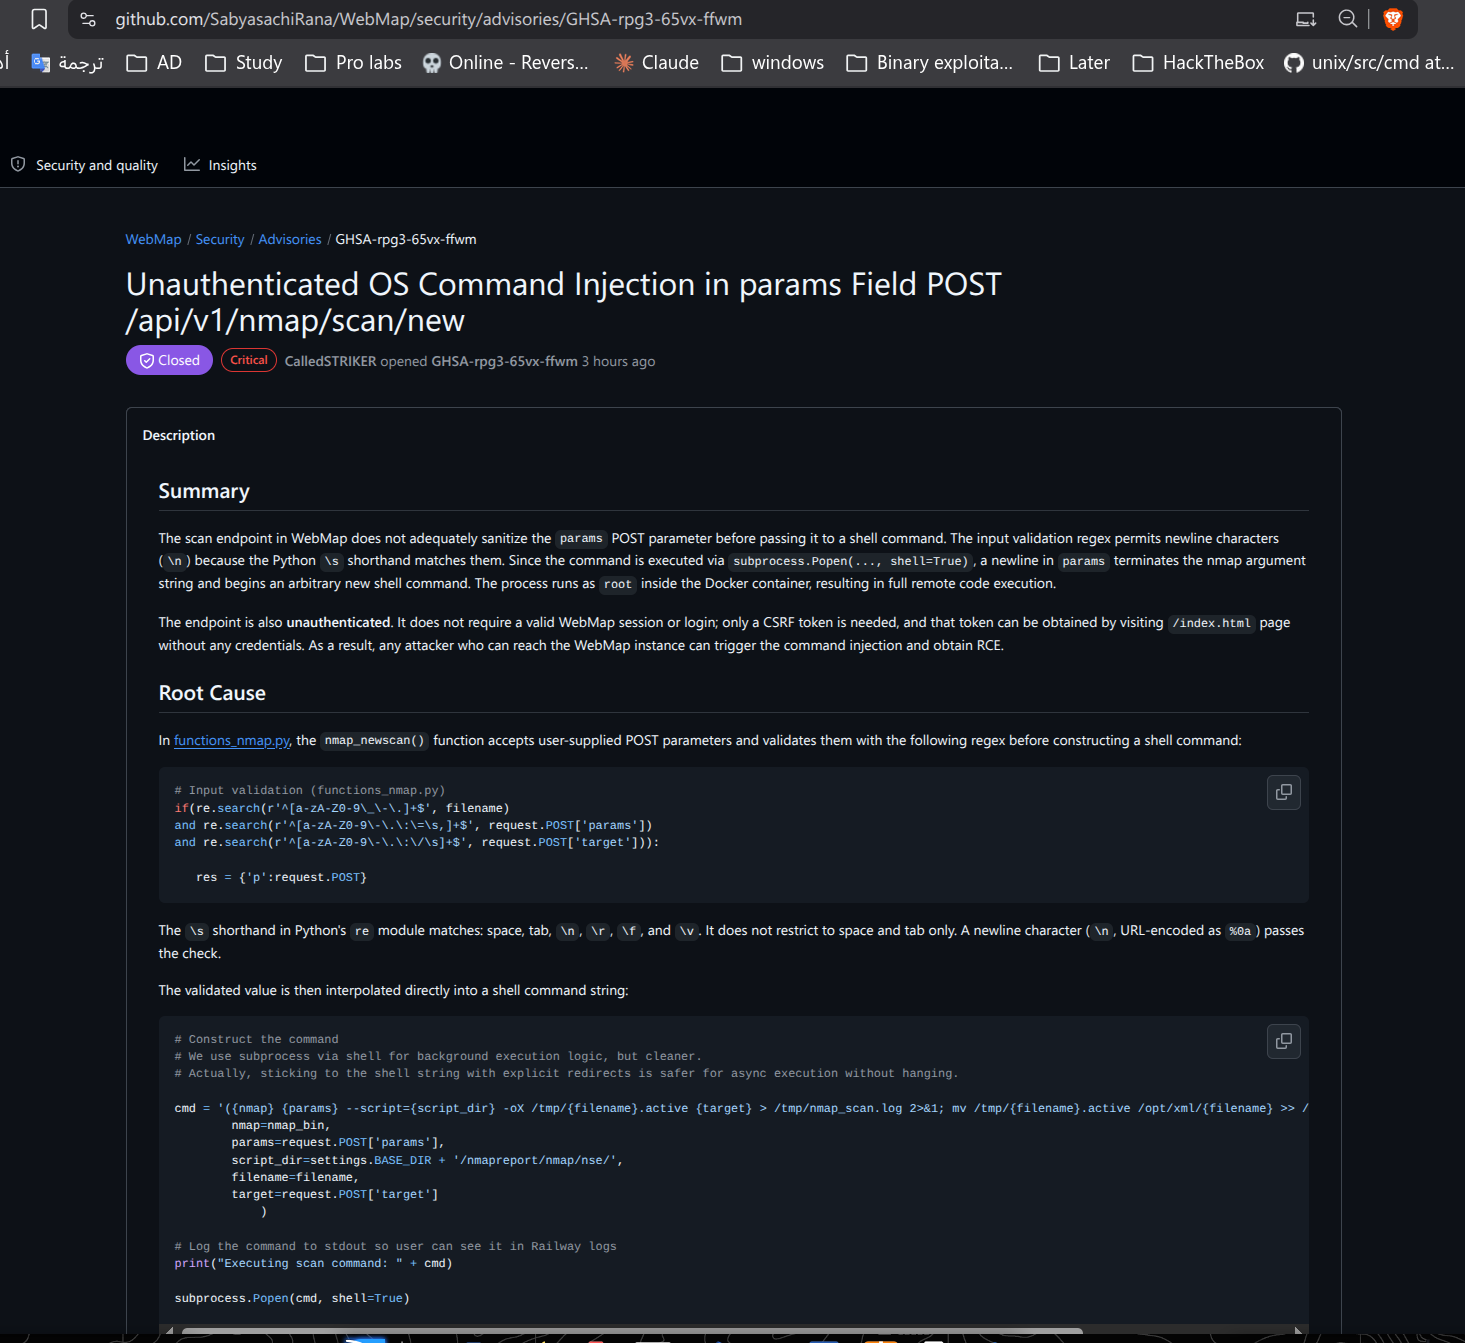
A security vulnerability has been detected in SabyasachiRana WebMap up to 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25. This affects the function nmap_newscan of the file functions_nmap.py of the component New Nmap Scan Handler. Such manipulation of the argument target/params leads to os command injection. The attack may be launched remotely. The exploit has been disclosed publicly and may be used. The name of the patch is 3d52f65803a2716bff14d938352c6fef45b0cfb6. A patch should be applied to remediate this issue. This issue got fixed with a silent patch.
Affected Software
| Vendor | Product | Version Range | Status |
|---|---|---|---|
| SabyasachiRana | WebMap | 8b95fe4dc301a3c09ddf145b895de0bf9f8d2a25 | affected |
Weaknesses
- CWE-78: OS Command Injection
- CWE-77: Command Injection
References
- https://vuldb.com/vuln/403395
- https://vuldb.com/vuln/403395/cti
- https://vuldb.com/cve/CVE-2026-90843
- https://vuldb.com/submit/925586
- https://calledstriker.gitbook.io/blog/security-research/webmap
- https://raw.githubusercontent.com/CalledSTRIKER/CalledSTRIKER-gitbook/refs/heads/main/security-research/2026-05-30_12-29.png
- https://github.com/SabyasachiRana/WebMap/commit/3d52f65803a2716bff14d938352c6fef45b0cfb6
- https://github.com/SabyasachiRana/WebMap/
Feedback
Was this page helpful?
Glad to hear it! Please tell us how we can improve.
Sorry to hear that. Please tell us how we can improve.